Cheat Sheet: 12 Best Practices for Developer-First Static Application Security Testing (SAST)
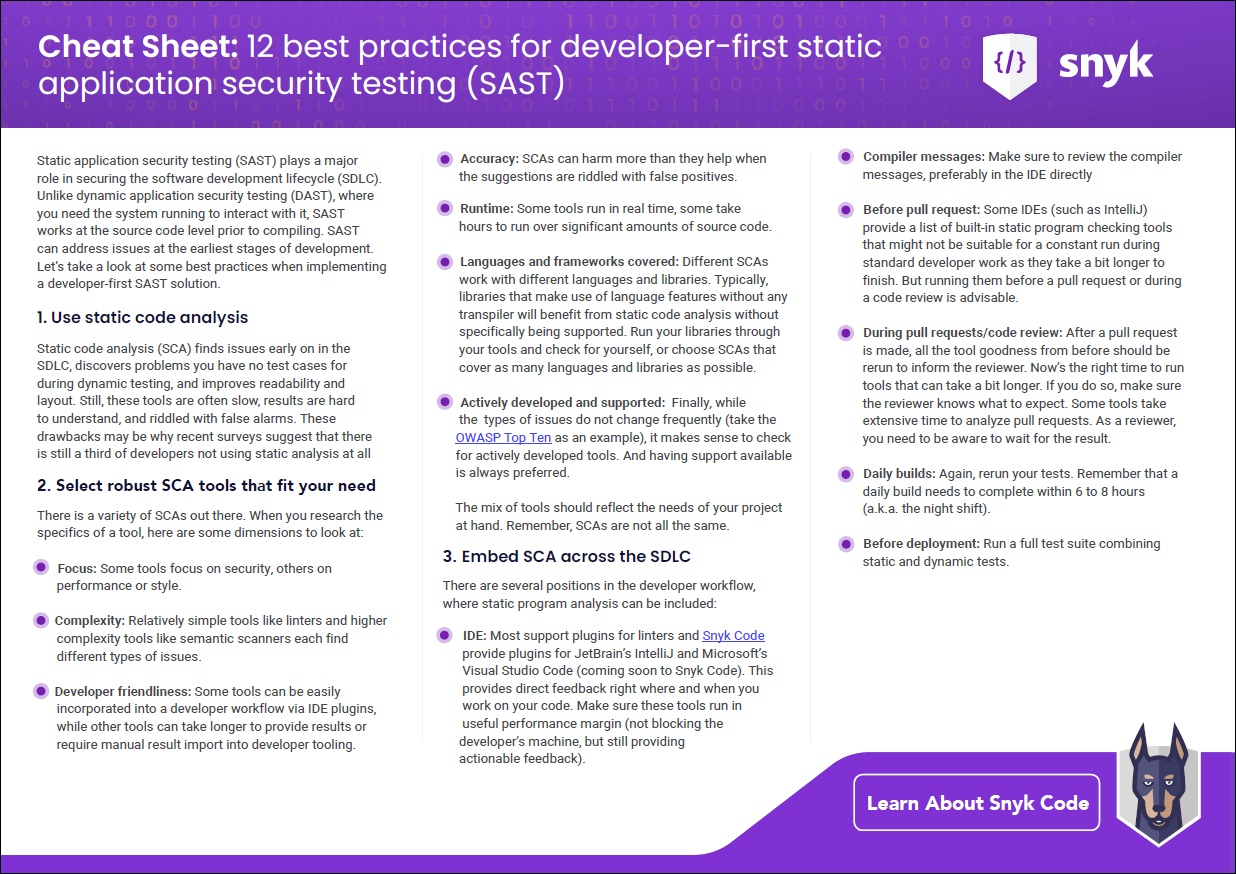
Static application security testing (SAST) plays a major role in securing the software development lifecycle (SDLC). Unlike dynamic application security testing (DAST), where you need the system running to interact with it, SAST works at the source code level prior to compiling. SAST can address issues at the earliest stages of development.
Download this cheat sheet to learn some best practices when implementing a developer-first SAST solution.